The North Korean Hacker Hired Through a Laptop Farm
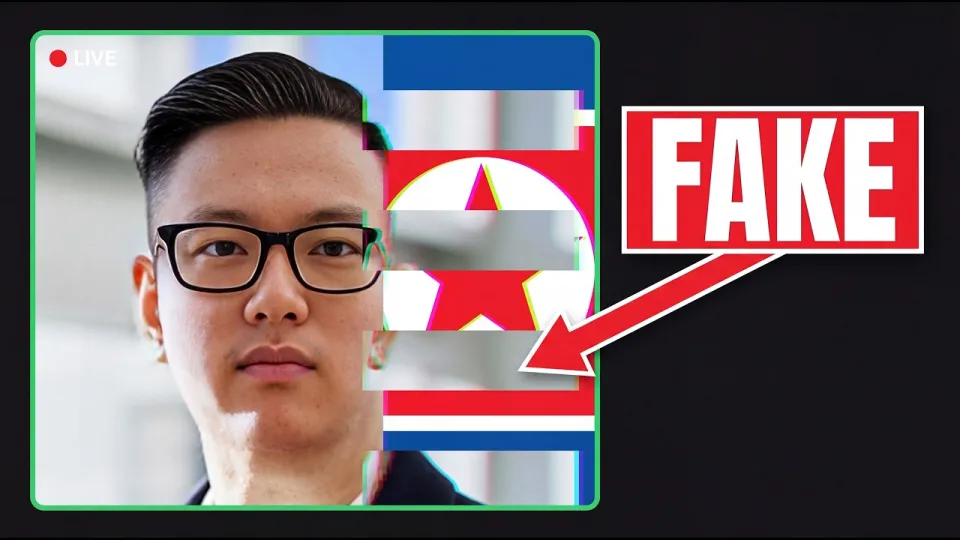
Video: Company Has No Idea Its New Hire Is a North Korean Hacker (crime story)
· based on the channel Max Crime
A crime story about North Korea's remote-work infiltration begins with a simple inversion: a company that trains employees to spot fakes hired one anyway. In 2024 the security-awareness firm KnowBe4 brought on a new software engineer who cleared four video interviews, a clean background check and a stolen American identity, and whose work laptop began loading malware the moment it was switched on. He was a North Korean IT worker, and the laptop farm that carried his traffic was run from a house in Arizona.
How a North Korean hacker gets hired at an American company
The mechanics of the scheme are deliberately boring, which is why it works. A DPRK operator buys or borrows a real U.S. identity, builds a plausible résumé, and applies for remote developer or IT roles at companies that never meet staff in person.
- Identity. The applicant uses a real American's name, address and Social Security number, often bought from data breaches. KnowBe4's own account notes the photo on the application had been altered with AI.
- Interviews. The candidate appears on video calls, sometimes with deepfake filters or a stand-in, and answers technical questions competently. KnowBe4 ran four separate interviews before making an offer.
- Background check. Because the identity is genuine, standard screening returns a clean result. There is no criminal record to find, because the person being checked is not the person being hired.
- The laptop. The employer ships a company machine to a U.S. address. That address belongs to a facilitator, not the worker.
- The connection. The facilitator plugs the laptop into power and internet. Remote-access software then lets an operator in another country log in from what looks like an ordinary American home IP address.
The laptop farm in an Arizona home
The crime story's physical evidence was wire shelving. Christina Chapman, a U.S. citizen living in Arizona, kept more than ninety company laptops in her home, each tagged with the name of the employer and the stolen identity it was registered to. She received the machines, kept them powered and connected, and forwarded the access to overseas operators.
Prosecutors said the arrangement was not a one-off favor. The Justice Department described a multi-year operation in which Chapman helped DPRK IT workers obtain remote employment at more than 300 U.S. companies, including Fortune 500 firms and at least one defense contractor. She was sentenced in July 2025 to 102 months in federal prison.
The money tells its own story. Chapman personally kept about $177,000, while more than $17 million in wages passed through her household. She maintained that she did not know who she was really working for; prosecutors pointed to her own messages as evidence she did. The victim companies in her case were not named by the Justice Department.
Why the salary money goes to Pyongyang
North Korea's IT worker program is a revenue operation, not a hacking spree in the ordinary sense. The workers hold legitimate jobs, collect legitimate paychecks, and route most of the money home. U.S. authorities have said the program generates hundreds of millions of dollars a year for the regime, funding weapons programs that sanctions are meant to starve.
The FBI's public service announcement in January 2025 warned U.S. companies directly about this pattern, describing thousands of DPRK IT workers embedded in remote roles worldwide. Microsoft tracks a related cluster of this activity under the name Jasper Sleet, which it linked in mid-2025 to intrusions at several organizations that had hired such workers. The threat is not only theft of wages: once inside, an operator has a trusted account, an internal email address and access to source code or customer data.
The night of the alert in Florida
The crime story's most instructive sequence is a timeline. At a Florida company, a newly issued work laptop began behaving abnormally almost immediately after it was set up, and the internal alert escalated within minutes rather than days. Between roughly 9:55 PM and 10:20 PM, responders isolated the machine, traced the remote-access tooling and confirmed that the human on the other end was not the person on the employment file.
That window matters because it shows where the defense actually lives. The fraudulent hire got through the résumé, the interviews and the background check; what stopped the intrusion was endpoint monitoring and a fast decision to cut the machine off the network. Companies that detect this behavior late typically discover it only when a payroll audit, a security review or the FBI comes knocking.
More houses, more laptops
Chapman's case was not an isolated household. Investigators who searched her home found the shelving, the tags and the shipping records, and the trail led to other addresses doing the same work. The FBI has described multiple laptop farms across the United States, including operations in Texas, where machines were kept running in residential rooms to preserve the appearance of American workers.
The economics explain the spread. A single embedded IT worker can earn a six-figure U.S. salary; a facilitator who hosts dozens of laptops takes a cut of each. The barrier to entry is low: a spare room, reliable internet, and a willingness to receive packages under other people's names.
They were both hired
The uncomfortable detail in this crime story is that two people were hired: the operator overseas, and the American who made the connection look local. Both passed through the same hiring funnel that was supposed to filter them out.
For employers, the practical lessons are concrete. Verify that the person on the video call matches the identity documents, and be suspicious of candidates who refuse to appear on camera or whose audio and lip movement drift apart. Check whether the shipping address for equipment matches the claimed residence. Watch for remote-access tools installed on day one, and for logins that always originate from one IP address while the employee claims to be elsewhere. Treat a newly hired engineer's first weeks as a monitored period, not a trusted one.
What the case leaves behind
A company that sells security training learned that training is not screening, and a woman in Arizona learned that hosting other people's laptops is a federal crime. The DPRK IT worker scheme persists because it exploits ordinary trust: a clean background check, a competent interview, a laptop delivered to a house. The full breakdown of the case, including the reconstruction of that night in Florida, is the work of the channel Max Crime, which assembled the account from Justice Department releases, the FBI notice, KnowBe4's disclosure and reporting by major U.S. outlets. The lesson for any employer is that the résumé is the weakest point of verification and the network is the strongest.
Key takeaways
- KnowBe4, a security awareness firm, hired a North Korean IT worker who passed four video interviews and a background check using a stolen American identity and an AI-altered photo.
- Christina Chapman of Arizona housed more than 90 company laptops on wire shelves in her home, each tagged with a company and a stolen name, and was sentenced to 102 months in federal prison in July 2025.
- Chapman personally kept about $177,000 while more than $17 million flowed through her operation, according to prosecutors.
- The FBI and Justice Department tied the scheme to DPRK IT workers, tracked by Microsoft as the threat group Jasper Sleet.
- The scheme works because the laptops sit on U.S. soil with U.S. IP addresses, so remote-access software connects the employer's machine to an operator overseas.
Questions & answers
How did a North Korean IT worker pass a background check at a security company?
The worker used a real American's identity, including name, address and Social Security number, typically bought from data breaches. Standard screening checks that identity and finds nothing wrong, because the person being checked is not the person applying. KnowBe4 also noted the application photo had been altered with AI.
What exactly is a laptop farm?
It is a U.S. location where company-issued laptops are kept powered on and connected to the internet. Remote-access software lets an operator abroad log in through an American IP address, so the employer sees an ordinary home connection. Christina Chapman kept more than ninety such machines on wire shelves in her Arizona home.
Where did the money from these fake jobs go?
Most of the wages were routed back to North Korea, which runs the IT worker program as a revenue source. In Chapman's operation, more than $17 million passed through her house while she personally kept about $177,000, according to prosecutors. She was sentenced to 102 months in federal prison.
Would our company catch a hire like this?
Only if screening goes beyond documents. Verify identity on camera, confirm that equipment shipping addresses match claimed residences, and monitor new hires for remote-access tools and logins from a single IP. In the Florida case, endpoint monitoring and a fast decision to isolate the laptop stopped the intrusion, not the interview process.
Source: Company Has No Idea Its New Hire Is a North Korean Hacker (crime story) · Markdown version